
The infamous ShinyHunters extortion group has leaked over 41 gigabytes of data allegedly stolen from the physical security firm Brinks Home.
Headquartered in Dallas, Texas, Brinks Home provides home security systems backed by an alarm response center.
Last week, the company announced that hackers accessed a portion of its IT systems and that they threatened to leak information allegedly stolen during the incident.
“We are aware that such material may be posted publicly. Brinks Home is working diligently to determine what information was involved and who may be affected,” the company said in an incident notice.
Noting that it would notify potentially affected individuals if their personal information was compromised, Brinks Home pointed out that customers should remain “vigilant against unsolicited emails, text messages, or phone calls requesting personal information or account credentials”.
According to Brinks Home, its alarm monitoring and system functionality has not been affected, as the attackers did not access its products or services.
The company has not shared details on the threat actor responsible for the incident, but its disclosure came around the same time that ShinyHunters added Brinks Home to its Tor-based leak site.
More than 4.9 million records were stolen from Brinks Home’s Salesforce instance during the incident, the extortion group says.
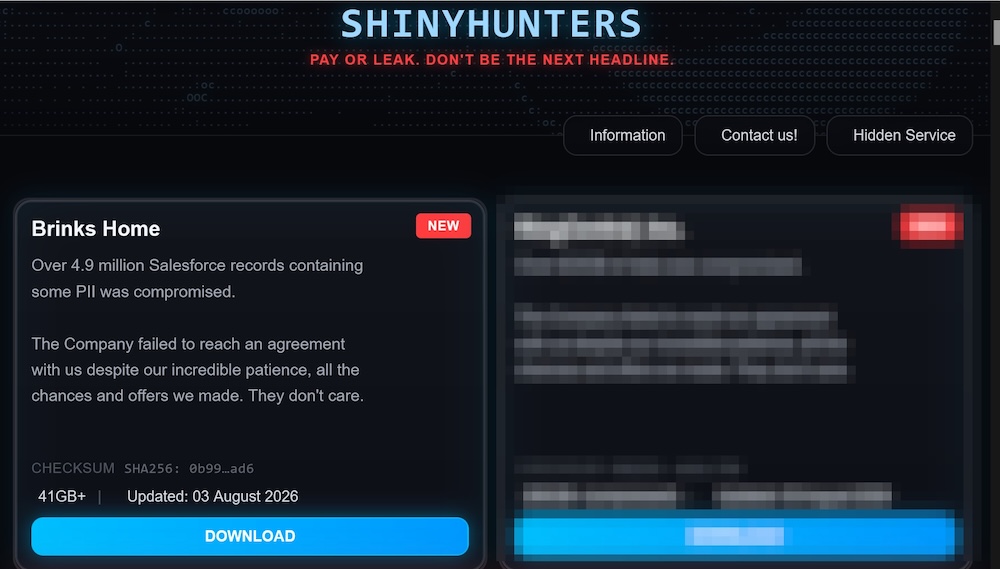
As the physical security firm did not pay a ransom, the hackers have leaked online more than 41GB of files allegedly stolen during the incident.
Some of the stolen records, ShinyHunters claims, include personally identifiable information (PII). SecurityWeek has not independently confirmed the hackers’ claims.
Related: Russian State APT Linked to Recent Public Wi-Fi Gateway Hacking
Related: CareCloud Data Breach Impacts Over 350,000
Related: Semiconductor Firm Analog Devices Discloses Data Breach
Related: ShinyHunters Claims Ernst & Young Hack






